TL;DR
Apache released HTTP Server 2.4.71 on November 11, 2026, fixing CVE-2026-119618, a critical mod_http2 flaw that Apache says can lead to remote code execution. Red Hat says public research has demonstrated a reliable exploit, although Wiz reported no known exploitation in the wild as of November 11. Administrators should check HTTP/2 configuration and apply the fixed release or their distributor’s security update.
The Apache HTTP Server project released version 2.4.71 on November 11 to fix CVE-2026-119618, a critical flaw in its mod_http2 module that Apache says can lead to remote code execution. The issue affects specified Apache and standalone mod_h2 versions, but exposure depends on whether a server has HTTP/2 enabled.

Get business pricing on monitors, keyboards and dev gear
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Apache describes the flaw as a shared-resource synchronization problem in the assign_headers() function, which handles HTTP/2 requests. Red Hat says a thread-safety weakness could let one thread change memory used by another, corrupting server memory. Red Hat rates the flaw CVSS 3.1 9.8 and says a remote attacker able to reach an affected server could run commands without authentication. Apache has not published exploit details.
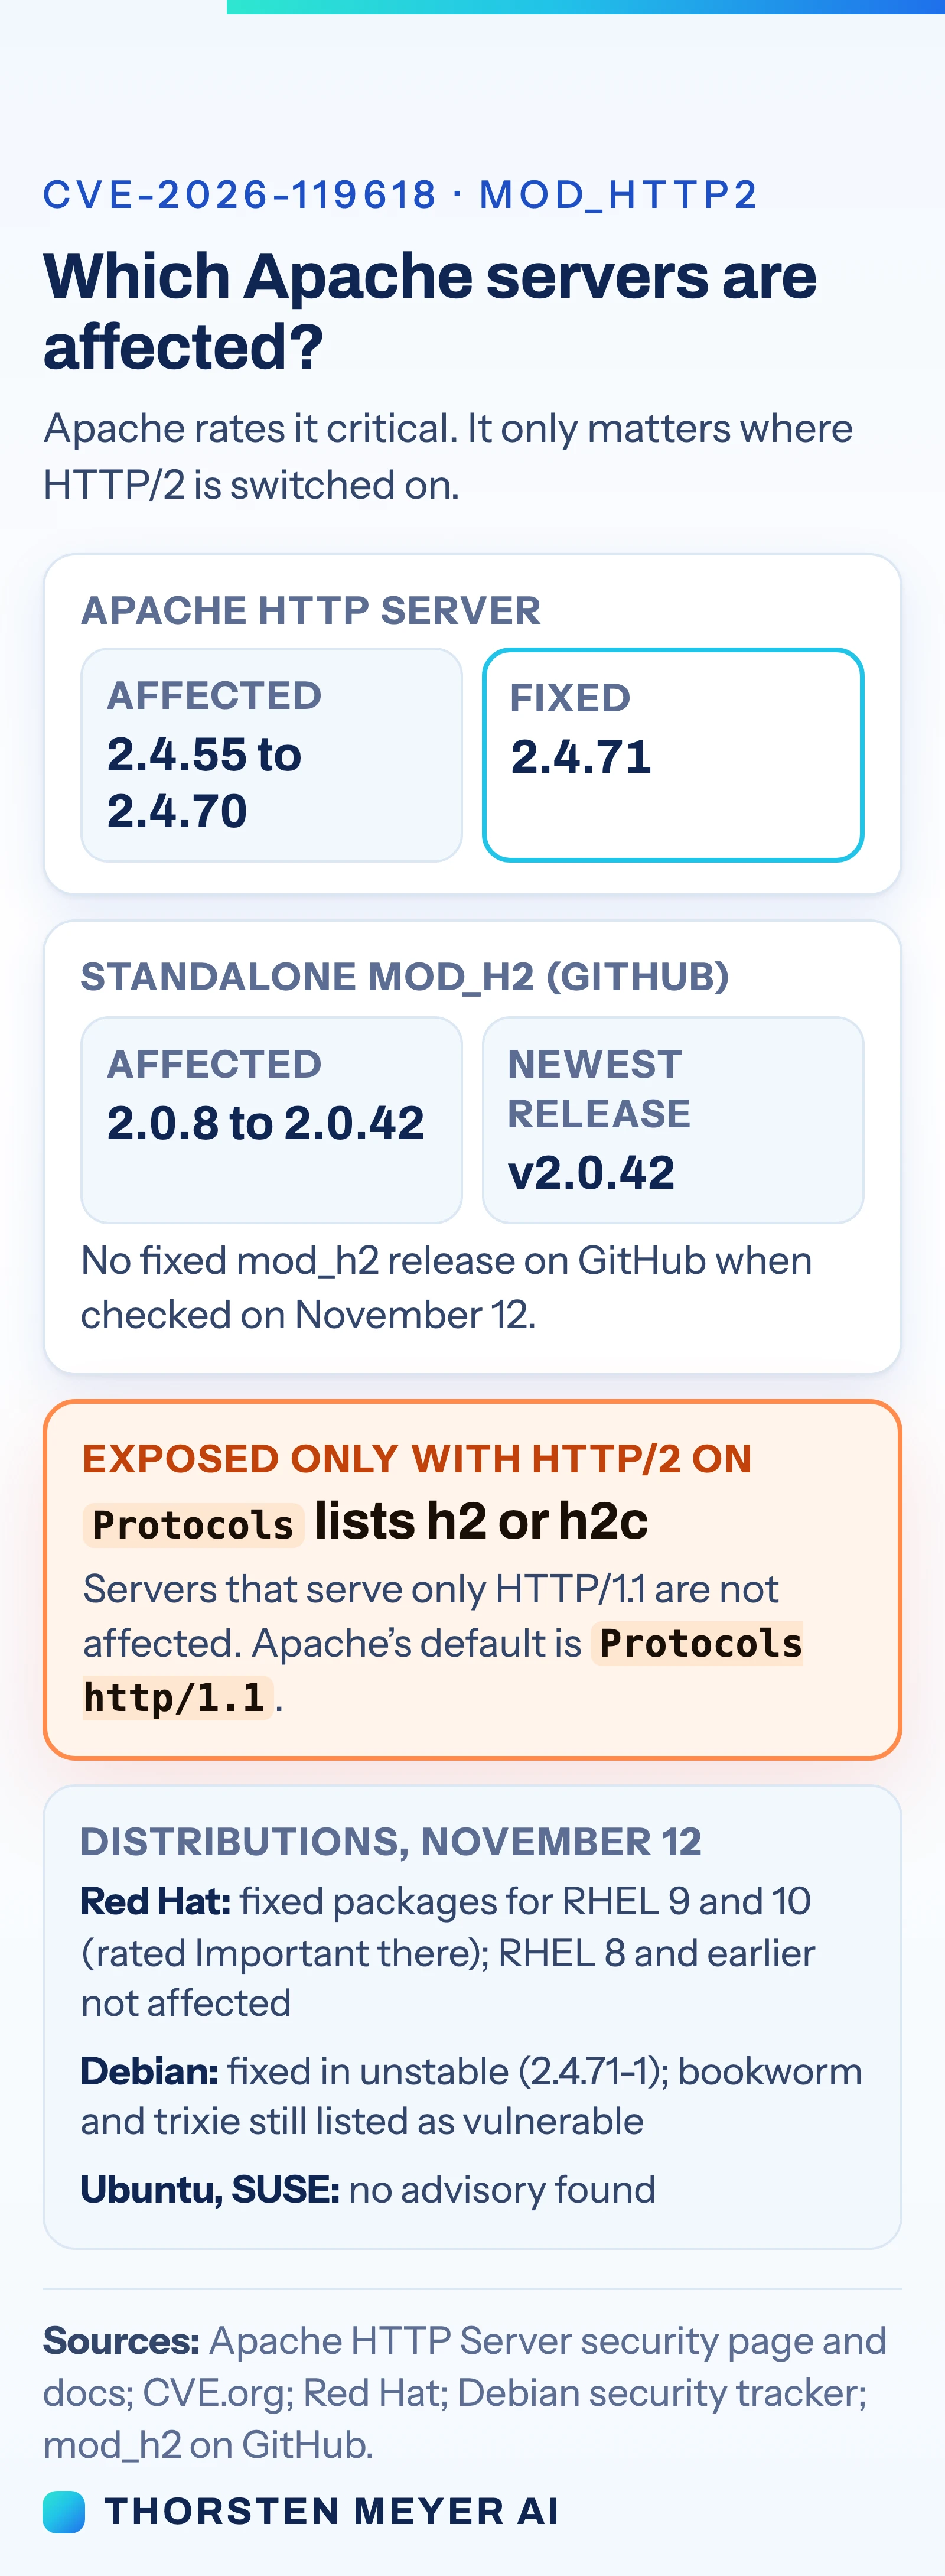
Apache lists HTTP Server 2.4.55 through 2.4.70 as affected and 2.4.71 as fixed. The standalone mod_h2 project on GitHub lists versions 2.0.8 through 2.0.42 as affected. Red Hat says servers with HTTP/2 protocols h2 or h2c enabled are affected; servers serving only HTTP/1.1 are not. Administrators should check their actual Protocols configuration.
Distribution status was uneven on November 12. Red Hat said fixed packages shipped November 11 for RHEL 9 and 10, while rating the issue Important for those versions; RHEL 8 and earlier were listed as unaffected. Debian listed bookworm and trixie as vulnerable, with version 2.4.71-1 available in unstable (sid). No Ubuntu or SUSE advisory had been found by the source publisher at that time. Red Hat JBoss Core Services and Red Hat Hardened Images remained listed as affected.
HTTP/2 Settings Determine Exposure
The flaw matters because HTTP/2 support is common in web server deployments, and Red Hat describes a potential path from network access to unauthenticated command execution. Apache documentation gives HTTP/1.1 as the default protocol setting, but operators may have enabled HTTP/2. The practical exposure question is therefore whether the affected component and version are present and whether h2 or h2c is active.
Wiz reported that 64% of its observed cloud environments had resources it considered vulnerable and 51% had publicly exposed instances. Wiz cautioned that its figures did not account for configuration. They describe the company’s customer data, not a count of servers confirmed exploitable, so they should not be read as global prevalence estimates.
Popular right now

iRobot Roomba 105 Combo Robot Vacuum & Mop with AutoEmpty Dock

iRobot Roomba Plus 405 (G181) 2-in-1 Vacuum and Mop Robot with AutoWash Dock

KitchenAid Artisan 5-Quart Tilt-Head Stand Mixer, Almond Cream
As an affiliate, we earn on qualifying purchases.
Reports Led to a November Patch
Apache credited the report to Anthropic’s OSS Scanner and two researchers from Google Cloud Vulnerability Research. According to the Apache timeline in the source material, Anthropic reported the issue on October 26 and the Google Cloud researchers reported it on November 3. The CVE number was reserved on October 30, according to the CVE.org record cited by the publisher. Apache issued the fix on November 11.
Many administrators receive Apache through a Linux distribution rather than directly from apache.org. Distribution packages can include different versions, backported fixes, or configurations, so package version numbers alone may not establish whether a system is patched. Operators should follow the security notice for their own distribution and product.
““Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server’s mod_http2 in assign_headers() can lead to RCE.””
— Apache HTTP Server project
Exploit Activity Remains Unconfirmed
Available statements differ on exploit status. Wiz said on November 11 that there was no available exploit and no reported exploitation in the wild. Red Hat said public research had demonstrated a reliable exploit against a default-configured server with mod_http2 enabled, but the source material gives no researcher identity or publication details. The publisher found no public exploit code linked from the cited advisories.
CISA’s Known Exploited Vulnerabilities catalog did not include the CVE when checked on November 12. The cited catalog version predated public disclosure, so its omission does not establish that exploitation has not occurred. The source material also did not provide an NVD score or published advisories from Ubuntu and SUSE at the time of checking.
Check Configurations and Vendor Advisories
Administrators should identify Apache HTTP Server and standalone mod_h2 deployments, check whether h2 or h2c is enabled, and install Apache 2.4.71 or the fixed package supplied by their operating system or product vendor. They should also review vendor notices for affected bundled products, including Red Hat JBoss Core Services and Red Hat Hardened Images.
Exploit reporting, CISA catalog entries, and distribution advisories may change as vendors investigate and publish updates. The available source material does not give a confirmed date for further advisories or a fuller account of the exploit research.
Key Questions
Which Apache versions are listed as affected?
Apache lists HTTP Server versions 2.4.55 through 2.4.70 and standalone mod_h2 versions 2.0.8 through 2.0.42 as affected. Apache HTTP Server 2.4.71 contains the upstream fix.
Does the flaw affect servers that use only HTTP/1.1?
Red Hat says servers serving only HTTP/1.1 are not affected. It identifies servers with h2 or h2c enabled through the Protocols directive as affected. Check the server’s active configuration.
Is CVE-2026-119618 being exploited?
The source material does not confirm exploitation in the wild. Wiz reported none as of November 11, while Red Hat said public research had demonstrated a reliable exploit. Those reports describe different evidence, and the status may change.
What should administrators install?
Use Apache HTTP Server 2.4.71 or the fixed package provided by the relevant operating system or product vendor. Distribution packages may include backported fixes, so consult the vendor’s advisory for the affected system.
Source: Thorsten Meyer AI